Professional services
A SOC readiness or detection coverage assessment, a SIEM deployment, or a detection use-case build for your in-house team to run.
Assess your detection coverage 04 / Managed SOC & MDR
Nueva's in-house security operations centre watches your environment around the clock, and acts when something is wrong.
Security tools generate alerts. Someone has to triage them, investigate them and respond, including at 2am on a Sunday. Most internal teams can't staff that. Many managed providers forward an alert and leave the response to you. The time between detection and containment is where an incident becomes a breach.
Nueva's SOC analysts monitor, investigate and respond across your endpoints, identities, cloud, email and network. It's Nueva's own team, not a partner's analysts under a Nueva badge. When a threat is confirmed, we contain it: isolate the device, disable the account, block the indicator. Then we bring in our incident response team if it needs to go further.
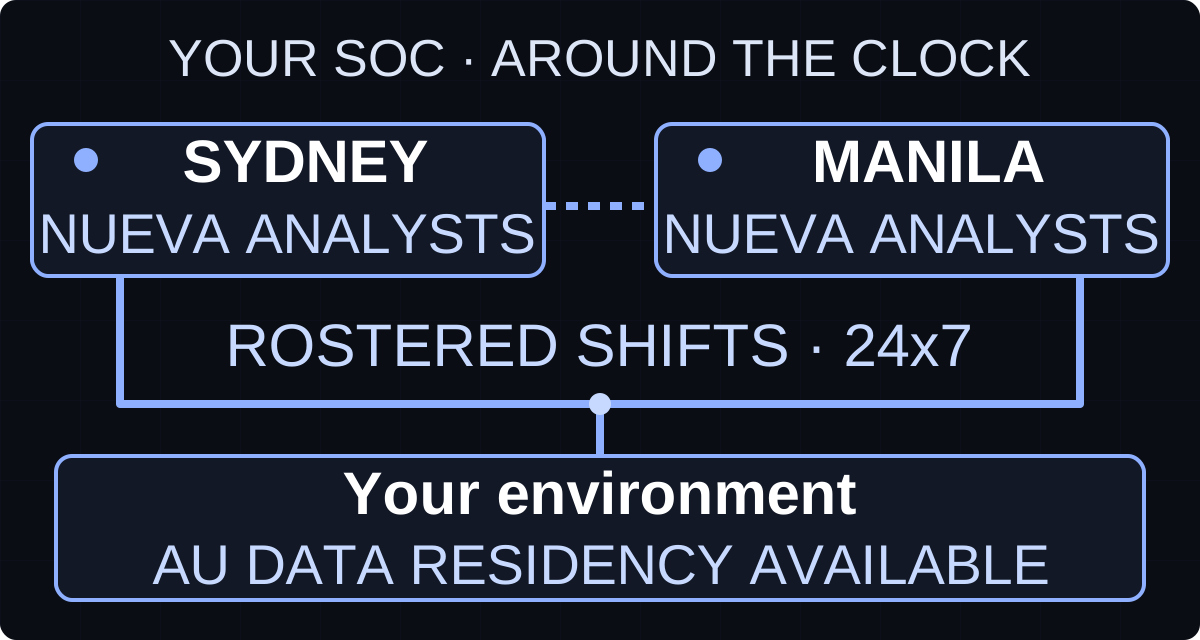
Nueva analysts on rostered shifts across Sydney and Manila, 24 hours a day, 7 days a week.
Before go live we agree, in writing, what our analysts may do without calling you first: isolate a device, disable an account, block an indicator. Anything beyond that, we call. You always get a written record of what was done and why.
Agreed in writing before go live. You get a written record of what was done and why.
Agreed in writing before go live. You get a written record of what was done and why.
Agreed in writing before go live. You get a written record of what was done and why.
Anything outside the agreed authority, we call before we act.
Our analysts watch around the clock, and our managed security and IT teams are ready to fix what they find.
We overlay what you own with our managed SIEM and 24x7 analysts, so you get more from the tools you already pay for.
We work with your people and build their skills, with incident response and security engineers on retainer when you need more.
Your security data is held in enterprise cloud security platforms, with Australian data residency available.
Get your detection ready with a project, or hand the watch to us.
A SOC readiness or detection coverage assessment, a SIEM deployment, or a detection use-case build for your in-house team to run.
Assess your detection coverageFull managed SOC & MDR. Our analysts work as your security operations team around the clock, monitoring, investigating and containing threats, and reporting back to your people.
Talk to our SOC teamBefore go live we agree, in writing, what our analysts may do without calling you first: isolate a device, disable an account, block an indicator. Anything beyond that, we call. You always get a written record of what was done and why.

Nueva brought the TWU's IT and security up to speed with the union and today's threats, and keeps them there.

Since 2020, securing corporate teams, franchisees and clubs across Asia through one approach to digital and physical security.

Continuous, independent assurance across PCI DSS, ISO 27001 and SOC 2, with one partner for security and cloud.
Call our incident team any time. If we can't answer straight away, leave a message and a responder will call you back as soon as possible.