 Client story / ROLLER
Security and compliance that keep pace with the product
How Nueva gives ROLLER continuous, independent assurance across PCI DSS, ISO 27001 and SOC 2, with one partner for its security stack and cloud.
- Client
- ROLLER
- Industry
- SaaS: venue management for attractions and leisure
- Frameworks
- PCI DSS · ISO 27001 · SOC 2 Type 1 and Type 2
- Practices
- Nueva Cyber
- Nueva Technology
- 3
- Compliance frameworks supported with ongoing, independent testing
- 4
- Exposure points protected: endpoints and identity, cloud, code and email
- 24×7
- Managed detection and response around the clock
- 1
- Partner across security, AWS and cloud marketplace procurement
“That gives us confidence the platform is secure every day, not just on audit day.”
A platform venues around the world rely on
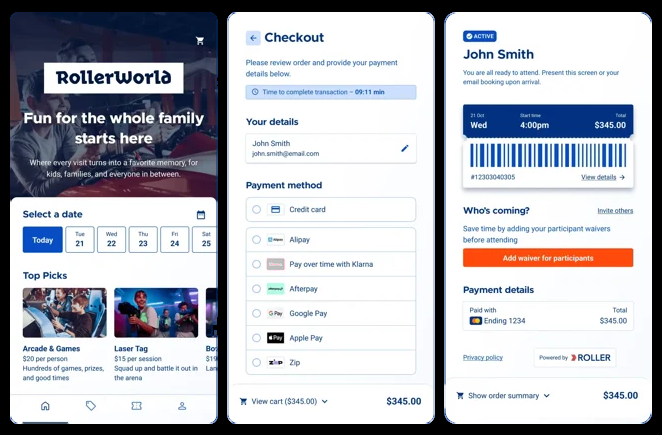
ROLLER is a cloud-based venue management platform built for attractions and leisure venues, from family entertainment centres and trampoline parks to zoos, aquariums and water parks.
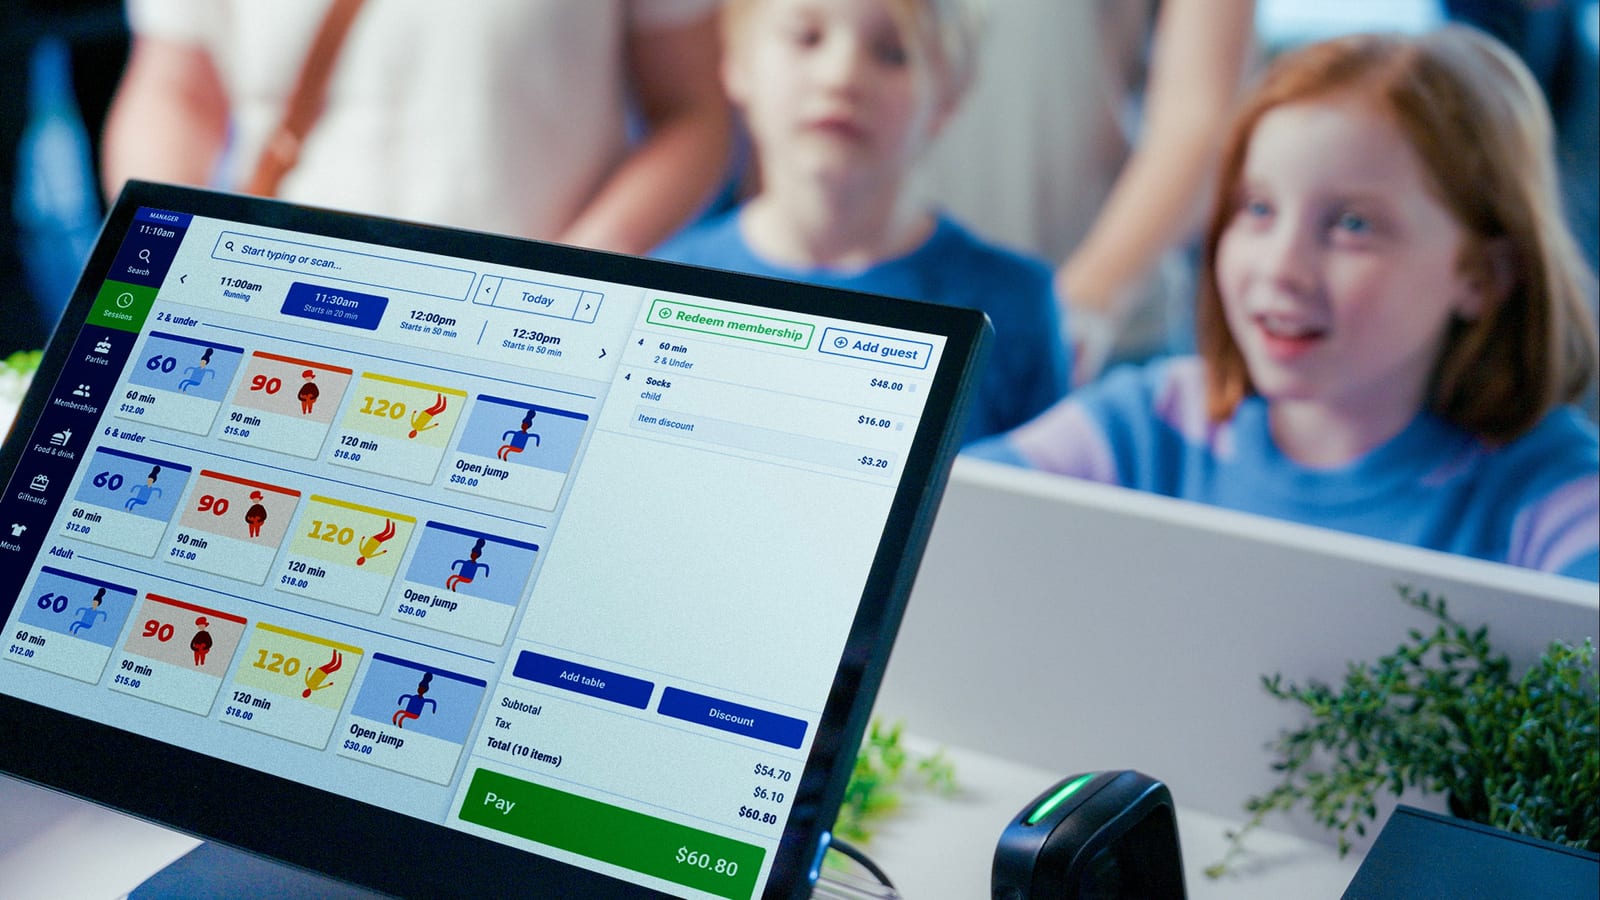
Its platform runs online ticketing, point of sale, memberships, waivers and the wider guest experience, which means it processes guest and payment data every day, for every customer.
Proving security, not just practising it
For a platform like ROLLER, customers expect evidence. PCI DSS, ISO 27001 and SOC 2 each call for regular, independent penetration testing and a clear record of how findings are fixed.
A single annual test doesn't suit a product that ships continuously.
ROLLER needed testing that kept pace with change, audit-ready evidence, and strong protection across endpoints, cloud, code and email, without adding more suppliers to manage.
Assure, protect and simplify
Four connected workstreams across two Nueva practices: prove security is working, protect where a SaaS business is most exposed, and make it simple to run.
- 01Nueva Cyber
Pen testing as a service
Rather than a one-off engagement, Nueva runs an ongoing penetration testing program aligned to ROLLER's framework obligations. Testing is scheduled around the release cycle, findings are prioritised by business risk, and fixes are retested, so every report doubles as audit evidence.
- PCI DSS
- ISO 27001
- SOC 2 Type 1
- SOC 2 Type 2
- 02Nueva Cyber
Compliance readiness
We work alongside ROLLER's team to prepare for audit: mapping controls to each framework, identifying gaps early and making sure the right evidence is in place before the auditors arrive, including the move from a SOC 2 Type 1 point-in-time report to Type 2 operating effectiveness.
- 03Nueva Cyber
Layered protection across the platform
Nueva designed and supplies a modern security stack that covers the places a SaaS business is most exposed.
- Endpoints and identityCrowdStrike MDR
Managed detection and response around the clock, so threats are found and contained quickly.
- Cloud and codeWiz
Visibility of cloud risk and code reviews that catch issues before they reach production.
- EmailAbnormal AI
Behavioural email security that stops phishing and account takeover attempts traditional filters miss.
- Endpoints and identityCrowdStrike MDR
- 04Nueva Technology
Cloud and procurement, simplified
Nueva resells and helps manage ROLLER's AWS environment, and handles procurement through the AWS and Google Cloud marketplaces. Security and cloud purchasing run through existing cloud agreements, with one partner accountable for both.
Every checkout, ticket and waiver runs on ROLLER.
Guest and payment data moves through the platform every day, so assurance has to be continuous, not occasional.
One partner for assurance, protection and cloud
- Business
Less to manage
Security, AWS and marketplace procurement through one relationship, so ROLLER's team can stay focused on the product.
- Assurance
Continuous assurance
Testing that keeps pace with the product, not a once-a-year snapshot.
- Compliance
Audit-ready evidence
Findings, fixes and retests mapped to PCI DSS, ISO 27001 and SOC 2.
- Security
Protection where it counts
Endpoints, cloud, code and email covered by a coherent stack.
“Security and compliance aren't optional for a platform like ours. Nueva's pen testing as a service gives us ongoing, independent assurance that maps directly to our PCI DSS, ISO 27001 and SOC 2 obligations, and they've helped us get audit-ready with confidence. Having one partner across our security stack and our AWS environment keeps things simple, so our team can stay focused on the product.”
The people who live it every day
“We ship continuously, so a once-a-year pen test was never going to give us the assurance we need. Nueva tests in step with our release cycle, prioritises findings by real business risk and retests every fix. That gives us confidence the platform is secure every day, not just on audit day.”
“Nueva helps us map our controls across PCI DSS, ISO 27001 and SOC 2, spot gaps early and have the right evidence ready before the auditors arrive. Every report shows findings, fixes and retests in one place, which is making our move from SOC 2 Type 1 to Type 2 far smoother.”
Services and technology
- Pen testing as a service
- Compliance readiness
- Managed detection and response
- Cloud and code security
- Email security
- AWS resale and management
- Cloud marketplace procurement
CrowdStrike · Wiz · Abnormal AI · AWS · Google Cloud
Shipping fast and need the evidence to match?
Talk to Nueva about continuous assurance, audit readiness and one partner across your security stack and cloud.